
Cloud Migration and Container Operations


Enabling Flipzen Cloud Migration and Scalable Container Operations on AWS
Flipzen is a fast-growing RegTech startup that uses artificial intelligence to automate compliance processes such as KYC, KYB, onboarding and document validation. By combining autonomous AI agents with collaborative workflows, it helps businesses across fintech, real estate and e-commerce streamline regulatory tasks.
As Flipzen scaled, the company decided to modernize its infrastructure and migrate to AWS, seeking improved scalability, centralized governance and cloud-native DevOps practices. binbash was engaged to architect and implement a secure AWS Landing Zone and to deploy a fully containerized platform on Amazon ECS on AWS Fargate, for both development and production.
Outgrowing a hand-provisioned cloud
Flipzen’s previous infrastructure setup posed several technical and operational limitations:
Lack of multi-environment governance and security best practices.
Fragmented container orchestration and scaling mechanisms.
Manual, inconsistent infrastructure provisioning.
Limited visibility and control over resource access, compliance and cost.
Executing a seamless migration of workloads and services to AWS with minimal disruption to ongoing operations.
A Landing Zone first, then serverless containers
binbash designed and implemented a secure, scalable AWS environment using its open-source Leverage™ framework and the AWS Well-Architected Framework. The engagement began with a multi-account AWS Landing Zone, establishing centralized governance, identity management via AWS IAM Identity Center, and access control through Service Control Policies.
binbash then provisioned Amazon ECS on AWS Fargate for both development and production workloads, enabling serverless container orchestration with autoscaling, secure networking and integrated Amazon RDS Aurora databases. All infrastructure was codified with Terraform, for repeatable, auditable deployments.
AWS Landing Zone Setup: A secure, scalable AWS Organization with dedicated accounts for management, security, shared services and application workloads (Dev and Prod), with centralized access via AWS IAM Identity Center and Service Control Policies.
Amazon ECS on AWS Fargate: Serverless container orchestration with ECS Fargate clusters in Dev and Prod, autoscaling enabled and load balancing through an ALB.
Amazon RDS Aurora: High-availability RDS clusters for persistent workloads in each environment, securely integrated with ECS and private networks.
Security and Compliance: CloudTrail, IAM Access Analyzer, GuardDuty and Security Hub across the organization, with baselines enforcing MFA, encryption by default and audit logging.
Automation & CI/CD Foundation: Every resource deployed via Terraform modules from the binbash Leverage™ framework, for repeatable, scalable and auditable infrastructure.
The entire engagement was fully subsidized through the AWS Startup Program, accelerating Flipzen’s transformation at no cost.
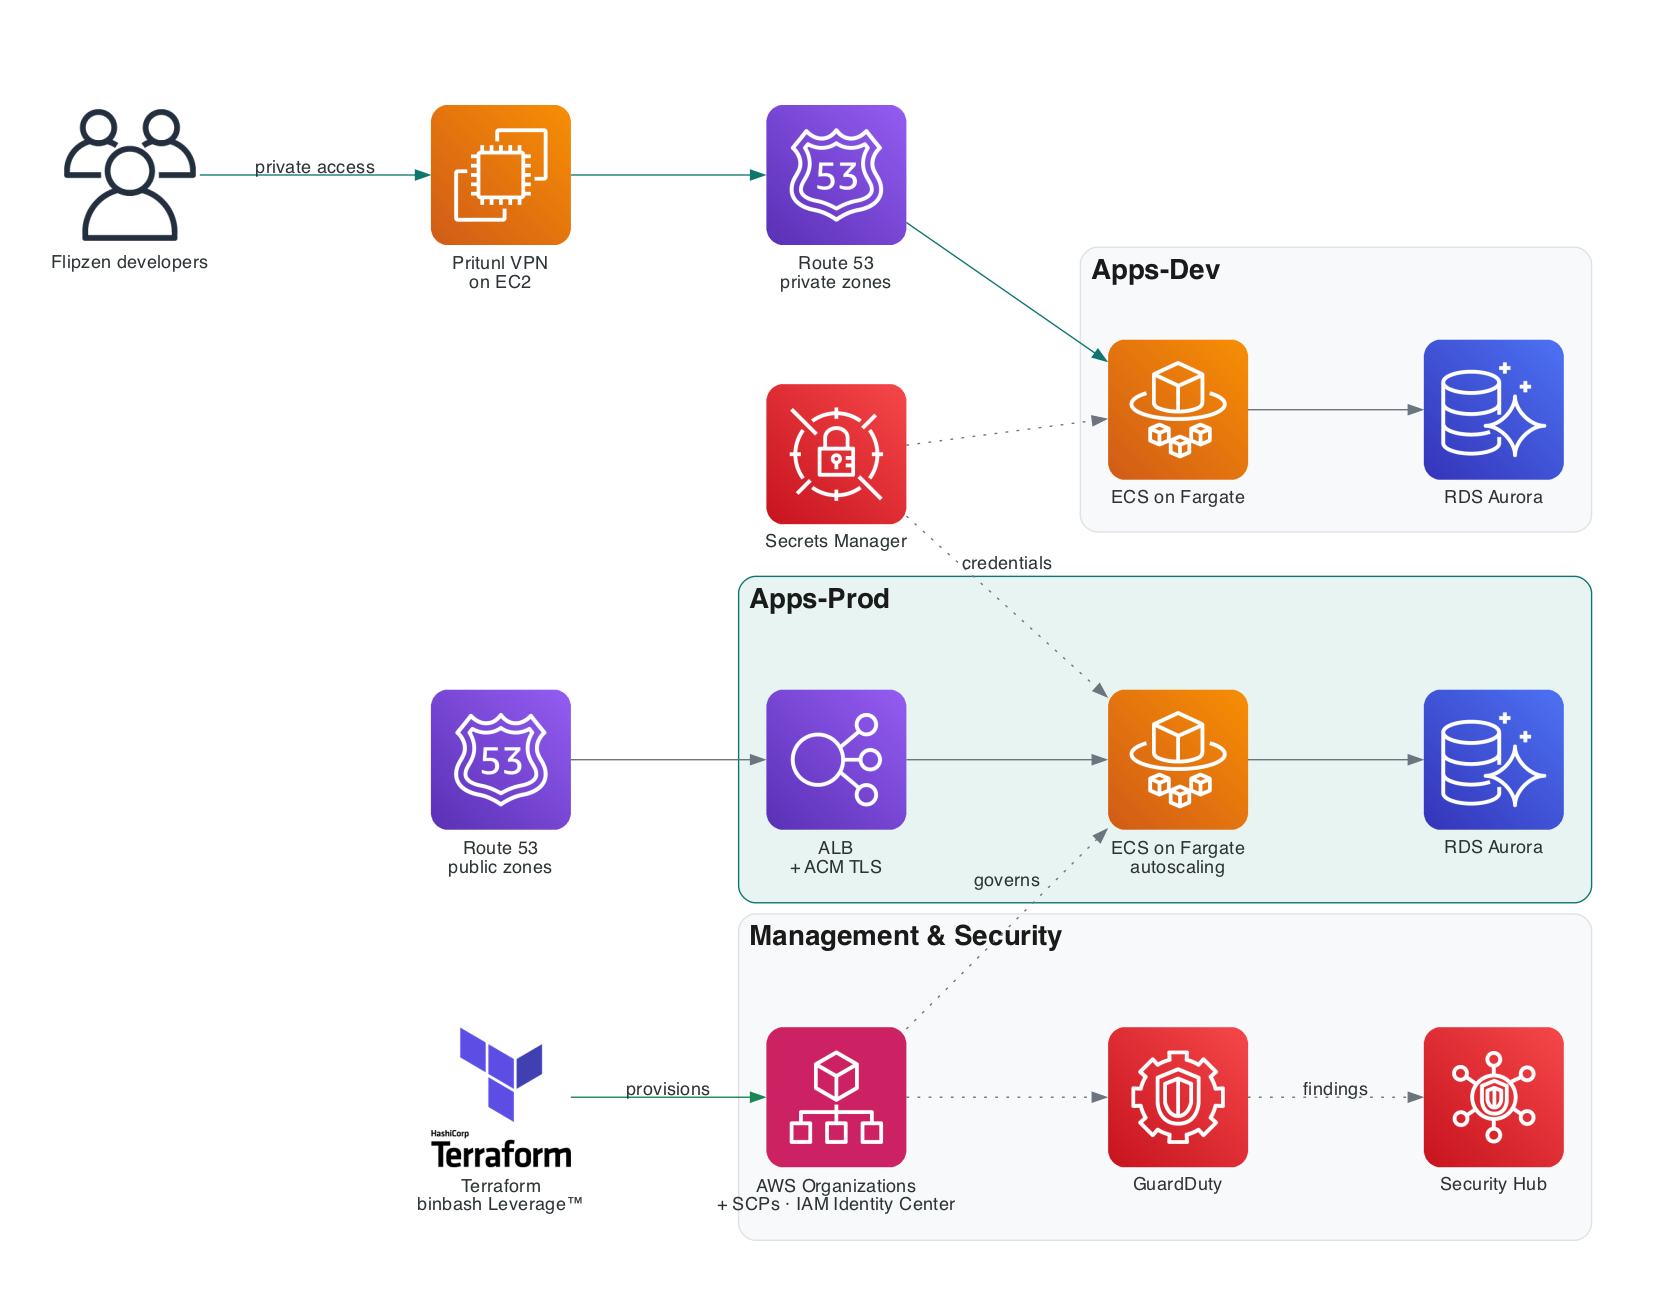
What Flipzen runs today
- $0
- cost to Flipzen, via the AWS Startup ProgramThe engagement was fully subsidized by the programme.
- 0
- disruption to operations during the migrationCore workloads moved off the previous cloud provider onto AWS.
- 100%
- of the platform codified in TerraformEvery resource from binbash Leverage™ modules — repeatable and auditable.
A successful migration of core workloads from a previous cloud provider to AWS, with zero disruption to operations.
Modernized cloud infrastructure with secure, centralized governance and automated provisioning.
Seamless container orchestration on ECS and Fargate, with environment-specific clusters.
Improved developer productivity via secure access, secrets management and infrastructure standardization.
An enhanced security posture through organization-wide monitoring, logging and IAM controls.
Delivered in four milestones
AWS Landing Zone Delivery: Account structure, baseline configurations, centralized SSO and Service Control Policies.
ECS Fargate Deployment (Dev & Prod): Scalable, container-based workloads with RDS, IAM and ALB integrations.
Secrets & VPN Implementation: Every service secured with AWS Secrets Manager, and safe infrastructure access enabled via VPN.
Monitoring & Security Framework: CloudTrail, GuardDuty and Security Hub activated, with Slack-based alerting on findings.
Cloud-native, and no vendor lock-in
Through its collaboration with binbash, Flipzen moved to a secure, modern and scalable platform built entirely on AWS and designed following the AWS Well-Architected Framework — with best practices around security, reliability, performance and cost optimization.